The following instructions explain how to set up the OpenVPN client of a Teltonika router with RutOS7 firmware for using the IP services 'mdex fixed.IP+ via OpenVPN' (security level 30) and 'mdex public.IP via OpenVPN' (security level 30).
Please note that the OpenVPN data throughput depends largely on the processing power of the router. The achievable bandwidth is significantly higher with the RUTX models than with the RUT2 and RUT9 models.
Setting up the OpenVPN client in the Teltonika router
Only the steps required to set up the OpenVPN client are described here, but not all the other router settings for the respective application.
- Please update the router to the latest firmware. Further information can be found here.
- First download the relevant OpenVPN configuration file by using 'right-click -> Save target as...':
- For 'mdex fixed.IP+': mdex fixed.IP30 Router.ovpn (right-click -> Save target as...)
- For 'mdex public.IP': mdex public.IP30 Router.ovpn (right-click -> Save target as...)
- Log in to the router; see also Local access to the router web interface (WebUI).
- It is recommended to perform a firmware update to the latest version. Further information can be found under Updating the Teltonika router/modem firmware.
-
Add the OpenVPN client according to the specifications of the respective firmware version:
From firmware version R_00.07.24 - Under Services -> VPN -> OpenVPN, add the OpenVPN client by clicking 'Add':
- Import the previously downloaded OpenVPN configuration file into the router with the following settings under 'OpenVPN configuration file' and add it by clicking 'Save & Apply'.
- Now click „Edit“ on the OpenVPN client and check under Authentication that „Password“ is selected.
- Under Security configuration, enter the username and password of the desired OpenVPN device and save all settings with 'Save & Apply'.
Up to firmware version R_00.07.06 - Under Services -> VPN -> OpenVPN, select the Role 'Client' and additionally enter a name under 'New configuration name', for example fixedIP or publicIP:
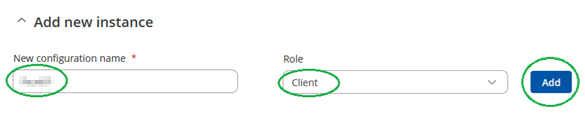
- Import the previously downloaded OpenVPN configuration file into the router with the following settings under 'OpenVPN configuration file'. The OpenVPN login details of the desired OpenVPN device must be entered under 'Username' and 'Password':
- Under Services -> VPN -> OpenVPN, add the OpenVPN client by clicking 'Add':
- The OpenVPN client has been set up and now establishes a connection to the mdex OpenVPN server.
- Under Network -> Firewall -> Zones (from firmware R_00.07.16), or Network -> Firewall -> General Settings (up to firmware R_00.07.06) , adjust the openvpn zone for Input to 'Reject':
If the 'openvpn' Input zone remains set to 'Accept', all router services are publicly accessible, which represents a considerable security risk, particularly when using a public IP address (mdex public.IP)!
- For the router and the end devices connected to it to be accessible remotely via 'mdex fixed.IP+', or 'mdex public.IP', openvpn must be set as the Source zone for all rules for remote router access and port forwards:
- Under Network -> Firewall -> Traffic Rules, use 'Edit' to adjust the relevant rules 'Enable_HTTP_WAN' (HTTP remote access) and 'Enable_HTTPS_WAN' (HTTPS remote access) to Source zone openvpn. Further information on activating remote access can be found here.
- Under Network -> Firewall -> Port Forwards, use 'Edit' to adjust the port forwards to Source zone openvpn. Further information on setting up port forwarding can be found here.